Research

Large-scale clinical and genomic data could drive predictive, preventive, personalized and participatory (P4) medicine, but privacy concerns keep most of it inside individual institutions. We develop privacy-preserving technologies that let federations of hospitals and research labs analyze data together, balancing usability, scalability and data protection.

Privacy-preserving biomedical data analysis

Analyses that need data from several hospitals or labs, carried out without revealing patient records to the other parties.

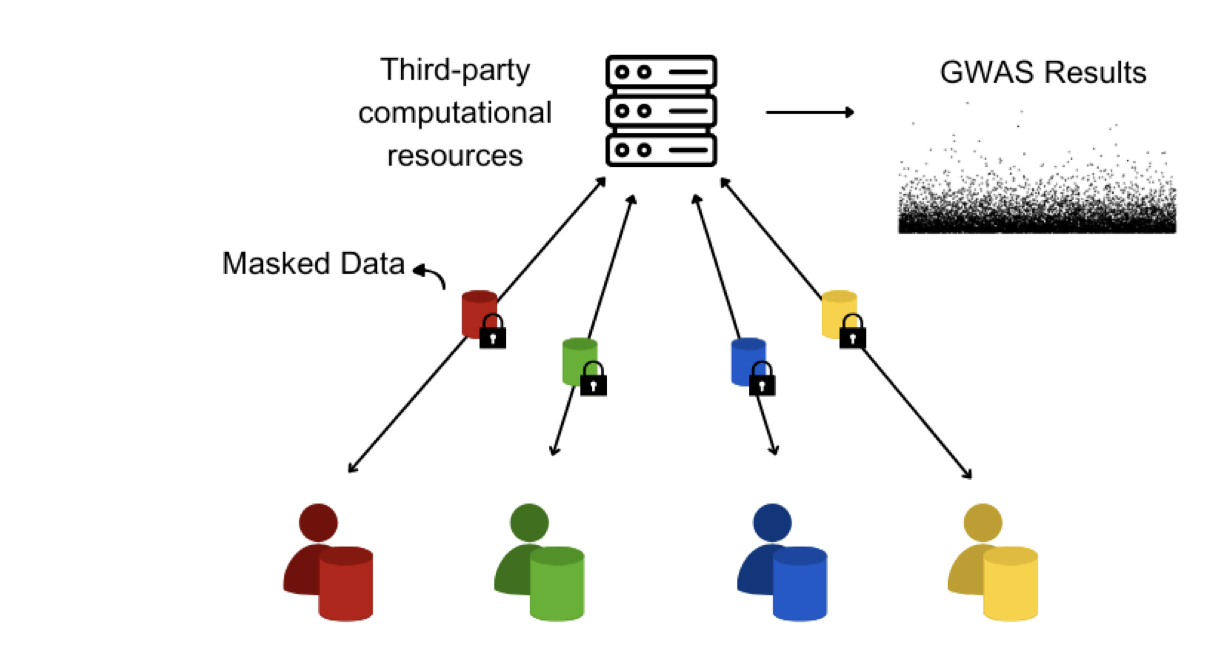
Diagram of masked data from several sites sent to third-party computational resources that return GWAS results
Figure from PP-GWAS: Privacy Preserving Multi-Site Genome-wide Association Studies (Nature Communications, 2025)

Genomics and rare diseases

Genomic data reveal information about individuals and their relatives, which makes sharing them across sites especially sensitive. We design privacy-preserving methods for genome-wide association studies that scale with cohort size and for querying whole-genome variant databases, and we support rare disease research across institutions: identifying disease-causing variants, analyzing rare disease variants under homomorphic encryption and detecting disease-associated cell subsets in single-cell data.

Key papers

Medical record linkage

Combining patient data from different sources can uncover new relationships between diseases and medical indications. We accelerate probabilistic privacy-preserving record linkage (PPRL) with three-party computation, so that records of the same patient can be matched efficiently and securely across institutions.

Key papers

Applied cryptography and secure computation

Cryptographic protocols that train, run and evaluate machine learning models on data that no single party can see, and hardware-based security for authentication and privacy.

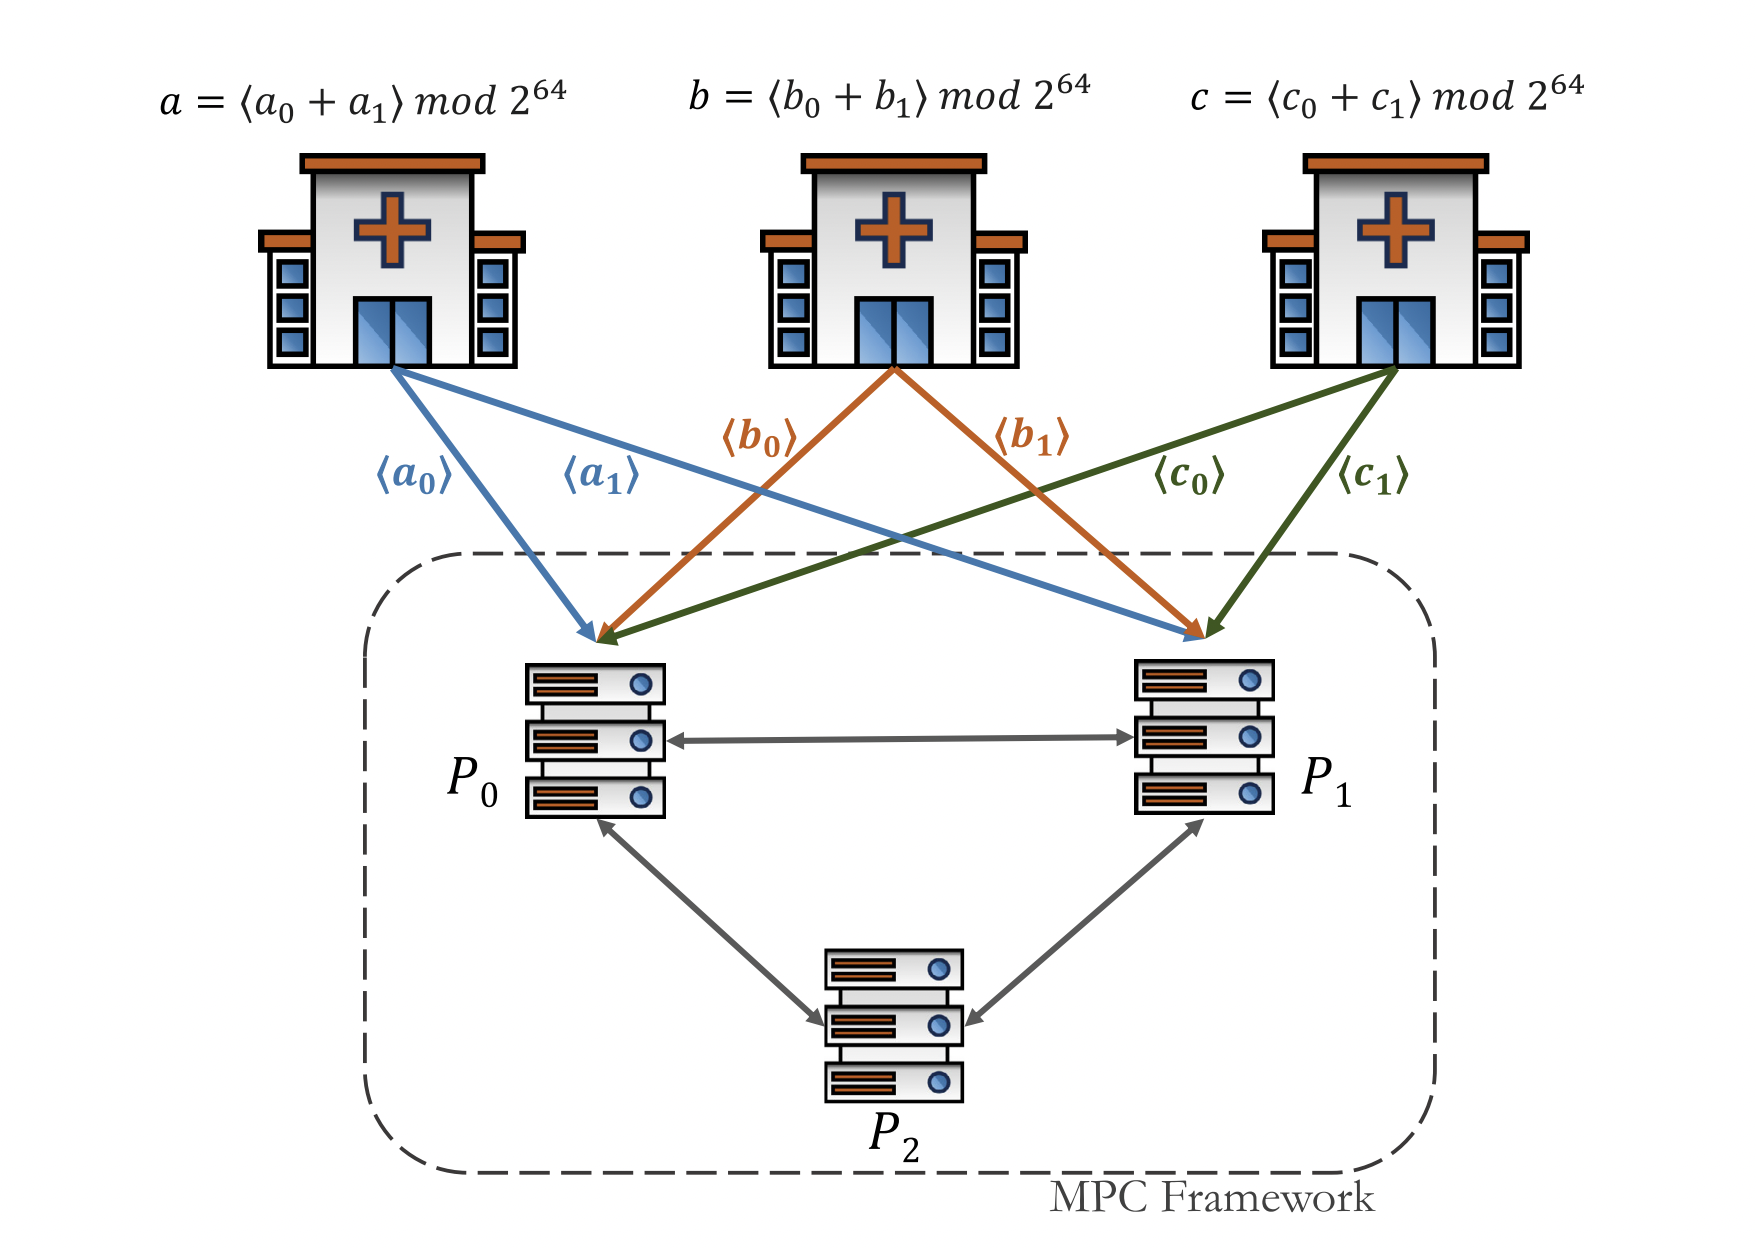
Three hospitals secret-share their data with two computing parties and a helper inside an MPC framework
Figure from Secure and Efficient Logistic Regression with Secret-Sharing MPC and Differential Privacy (IEEE Access, 2025)

Secure computation frameworks

We build frameworks for computing on data that no single party can see. CECILIA, our three-party computation framework, extends privacy-preserving machine learning beyond convolutional neural networks to recurrent kernel networks (RKNs), long short-term memory networks (LSTMs) and generative adversarial networks (GANs). We also develop secret-sharing protocols for training models such as logistic regression and support vector machines and for imputing missing medical data, and randomized-encoding approaches that make kernel computations on distributed medical and image data fast and scalable.

Key papers

Collaborative model evaluation

We develop methods that let clients evaluate machine learning models on pooled test data without compromising privacy, for example by computing ROC and precision-recall curves securely. This matters for clients with limited data who need to assess models trained on aggregated datasets, and it supports collaborative settings such as federated learning and the PHT-meDIC platform for distributed medical analytics.

Key papers

Hardware-based security

We design security protocols that build on hardware: physically unclonable functions (PUFs) for second-factor authentication and scalable RFID authentication, and trusted execution environments for a privacy-preserving smart grid.

Key papers

Federated and trustworthy machine learning

Learning across institutions without pooling data, and understanding when models leak information or can be attacked.

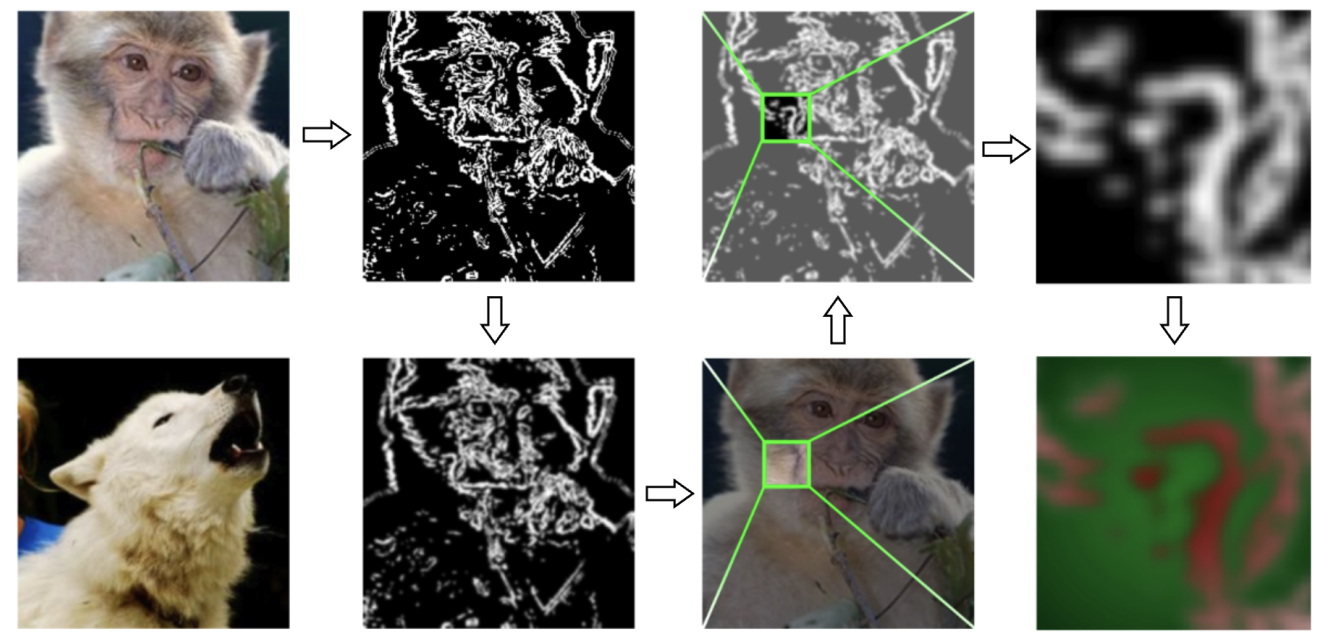
Source and target images with edge maps, illustrating a targeted adversarial attack
Figure from Accelerating Targeted Hard-Label Adversarial Attacks in Low-Query Black-Box Settings (SaTML, 2026)

Federated learning

We address the privacy challenges of federated learning with high-dimensional medical data and develop frameworks that keep model updates and data protected throughout collaborative training. This includes federated domain adaptation for sites whose data follow different distributions, and applications such as epileptic seizure prediction from EEG data, diagnosis of rare genetic syndromes from facial images, age prediction from DNA methylation data and the collective defense of IoT networks.

Key papers

Explainable machine learning

Model explanations can expose sensitive training data. We study these privacy risks and design methods that provide insightful explanations while protecting the individuals whose data was used in training, making machine learning models more trustworthy.

Secure and trustworthy AI

We study how machine learning models can be attacked and defended: targeted adversarial attacks in black-box settings with few queries, defenses against model inversion attacks, and the geometry of image classifiers' decision regions. We also work on protocol-level safeguards for trustworthy agentic AI systems.

Key papers

Core techniques

Secure multi-party computation
Several parties compute a result together while each keeps its own input private.
Homomorphic encryption
Computation runs directly on encrypted data; only the key holders can read the result.
Differential privacy
Calibrated noise limits what any released result reveals about a single individual.
Federated learning
Models are trained where the data lives; only model updates leave each site.

Funded projects

  • PriRare

    Exploring privacy-preserving solutions for rare disease analysis

    German Research Foundation (DFG)

  • PrivateAIM

    Federal Ministry of Education and Research (BMBF)

  • MDPPML

    Federal Ministry of Education and Research (BMBF)

Work with us

We welcome collaborations with clinical and academic partners, research visits and strong PhD and postdoc applications.

Ways to work with us All publications