Medical Data Privacy and Privacy-Preserving Machine Learning
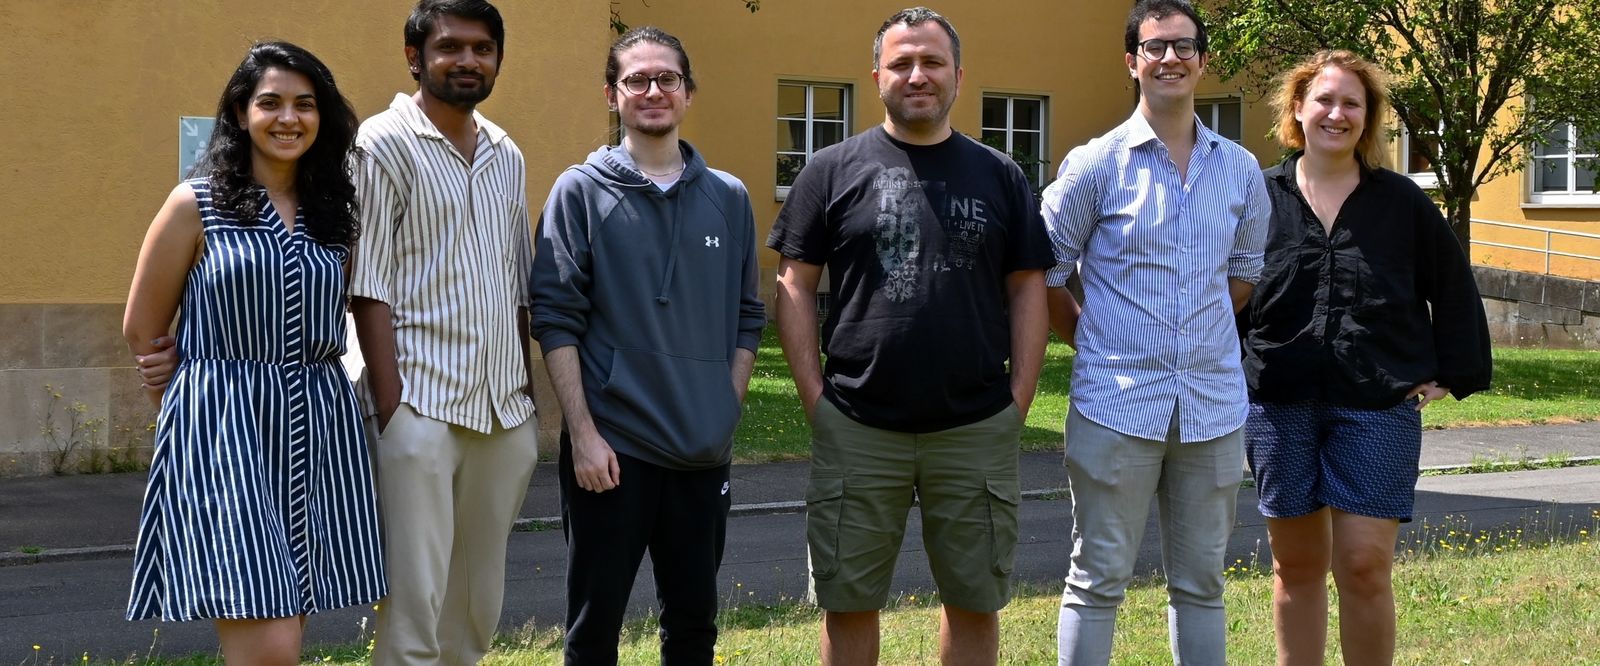
We develop methods that let hospitals and research labs analyze clinical and genomic data together, with machine learning and statistics, without exposing the patients behind it. We are a research group at the University of Tübingen.
What we work on
All of it is privacy-preserving: institutions get joint results without handing over patient data.
- Genomics and rare diseases
- Genome-wide association studies, variant queries and rare disease analysis across sites, without exposing patients' data.
- Medical record linkage
- Matching records of the same patient across sources to uncover new relationships between diseases.
- Secure computation frameworks
- CECILIA, our three-party MPC framework, plus secure training, data imputation and fast randomized-encoding methods for medical data.
- Collaborative model evaluation
- Letting clients evaluate models on pooled test data, such as computing AUC, without exposing that data to each other.
- Hardware-based security
- Authentication with physically unclonable functions, and privacy for smart grids with trusted execution environments.
- Federated learning
- Training models across institutions without pooling data, from domain adaptation to seizure prediction and rare-syndrome diagnosis.
- Explainable machine learning
- Model explanations that stay useful without leaking the training data behind them.
- Secure and trustworthy AI
- How machine learning models can be attacked and defended, and what makes AI systems, including agentic ones, trustworthy.
Recent papers
-
Privacy-Preserving Detection of Rare Disease-Associated Cell Subsets via Secure Multi-Party Computation
-
Empirical Evidence for Simply Connected Decision Regions in Image Classifiers
-
Unsupervised Multi-Source Federated Domain Adaptation under Domain Diversity through Group-Wise Discrepancy Minimization
-
Position: Trustworthy Model Context Protocol Enables Responsible Agentic AI!
News
-
Two ICML 2026 acceptances!
We are happy to share that our papers Unsupervised Multi-Source Federated Domain Adaptation under Domain Diversity through Group-Wise Discrepancy Minimization and Position: Trustworthy Model Context Protocol Enables Responsible Agentic AI! were accepted to ICML 2026.
-
A SaTML acceptance!
We are happy to share that our paper Accelerating Targeted Hard-Label Adversarial Attacks in Low-Query Black-Box Settings is accepted to SaTML 2026.
-
A Nature Communications publication
We are happy to share that our paper PP-GWAS: Privacy Preserving Multi-Site Genome-wide Association Studies is accepted to Nature Communications.
-
An IEEE Access publication!
We are happy to share that our paper Robust Representation Learning for Privacy-Preserving Machine Learning: A Multi-Objective Autoencoder Approach is accepted to IEEE Access.
Join the group
We welcome strong PhD and postdoc applications, research visits and collaborations in privacy-preserving machine learning for medicine.